Reporting to the NCSC
New Zealanders can report cyber security incidents to the NCSC through an online portal, which enables us to provide advice about the recommended next steps to those affected. The NCSC receives incidents of all sizes - from phishing sightings up to major cyber security breaches.
Incident triage
The NCSC handles cyber incident reports through two distinct triage processes. Most incident reports are managed through the NCSC’s general triage process.
A small number of cyber incidents are triaged for specialist technical support due to the nature of the victim or the seriousness of the incident. These incidents could cause high impact at the national level and are referred to as incidents of potential national significance. These may be incidents affecting organisations such as operators of critical infrastructure, and incidents that have the potential to impact large groups of New Zealanders.
The following section presents an analysis of incidents reported to us during the period from 1 July 2025 to 30 June 2026. Due to the way incidents are dealt with, some analysis is only available for certain subsets of the data.
Why report?
Any person or organisation in New Zealand can report incidents to the NCSC, to obtain help and guidance. We can help you understand what has happened, stop the incident getting worse, and help you get back on your feet. Reporting also provides us with information about the threat landscape, which we can use to issue advisories and alerts, or take disruptive action.
Severity and sector breakdowns
In 2025/26, the NCSC received a total of 4,673 reports. Individuals made 3,627 reports and organisations were responsible for 671 reports. The remaining did not specify the reporter.
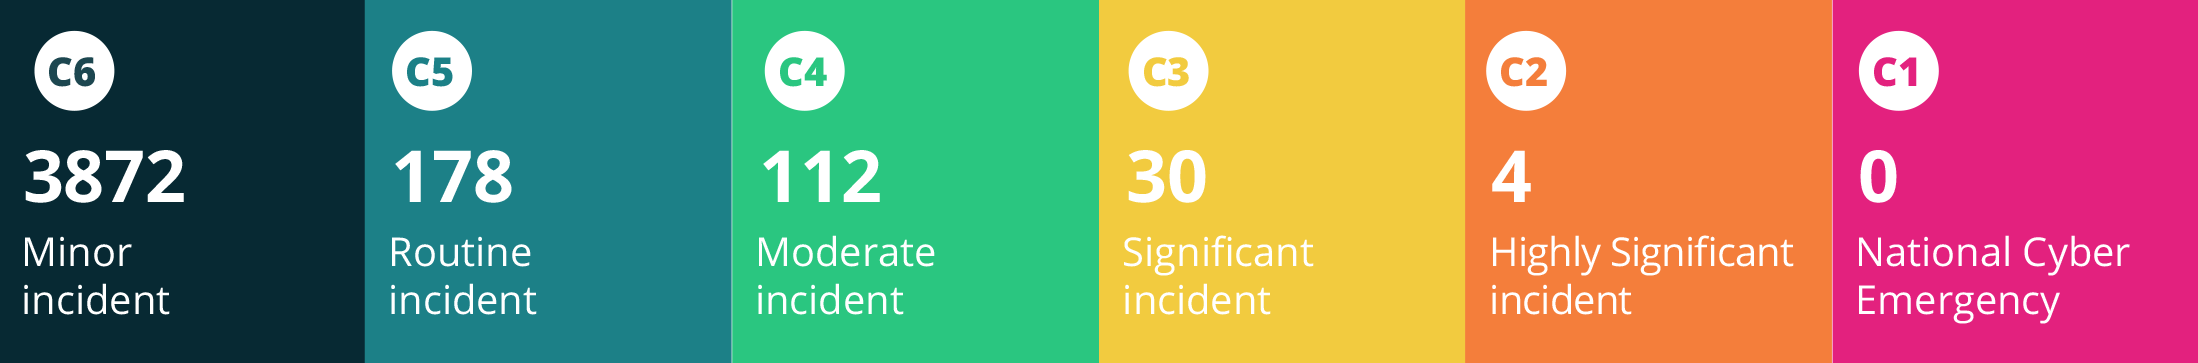
While the total number of cyber incidents reported to the NCSC has declined since 2021 the number of incidents of potential national significance has remained at a similar level. Furthermore 2025/26 saw four incidents classified as C2, or highly significant. The overall decline in reporting of lower severity incidents may reflect a number of factors including the integration of CERT (Computer Emergency Response Team) into the NCSC, changes to how the reporting of phishing incidents is managed and increased reporting of incidents directly to businesses (e.g. customers reporting directly to banks rather than to NCSC) or to other relevant agencies such as the Department of Internal Affairs and New Zealand Police
Incident severity
The NCSC triages incidents into six categories ranging from C1 (national cyber emergency) to C6 (minor incident).
In the 2024/25 year, the most severe incidents were categorised as C3. These incidents included several DDoS incidents that were likely linked to ideologically motivated malicious cyber activity, and ransomware incidents that had links to criminal or financially motivated actors. There was also a significant incident involving the network compromise of a New Zealand organisation, which had links to state-sponsored actors.
A national cyber emergency (C1) is defined as an incident that causes severe disruption to a core New Zealand service, and/or affects key sensitive data, and/or undermines the economic or democratic stability of New Zealand. At the other end of the scale, a minor incident (C6) is defined as an incident causing a known or likely impact on an individual/individuals, or precursor activity against an individual/individuals or a small or medium enterprise. In the middle, a significant incident (C3) is defined as an incident causing a known or likely impact on a large commercial enterprise, wider government, or supply chain to core New Zealand services.
Highly significant incidents (C2) consume substantial time and resources, but even significant (C3) or moderate incidents (C4) can take weeks to resolve and will generally involve complex responses involving several teams. For minor or routine incidents (C5 or C6), the NCSC might respond by providing general advice or alerts to customers.
Incident breakdown by severity
Sector breakdown
The following list shows the sector breakdown of the 4,304 incidents handled through our general triage process:
- Agriculture, Forestry and Fishing: 23
- Arts, Recreation and Other Services: 42
- Construction: 39
- Education and Training: 56
- Electricity, Gas, Water and Waste Services: 28
- Financial and Insurance Services: 54
- Health Care and Social Assistance: 53
- Individual: 3627
- Information Media and Telecommunications: 32
- Manufacturing: 48
- Mining: 1
- Professional, Scientific, Technical, Administrative and Support Services: 81
- Public Administration and Safety: 102
- Rental, Hiring and Real Estate Services: 11
- Retail Trade and Accommodation: 51
- Technology: 18
- Transport, Postal and Warehousing: 22
- Wholesale Trade: 10
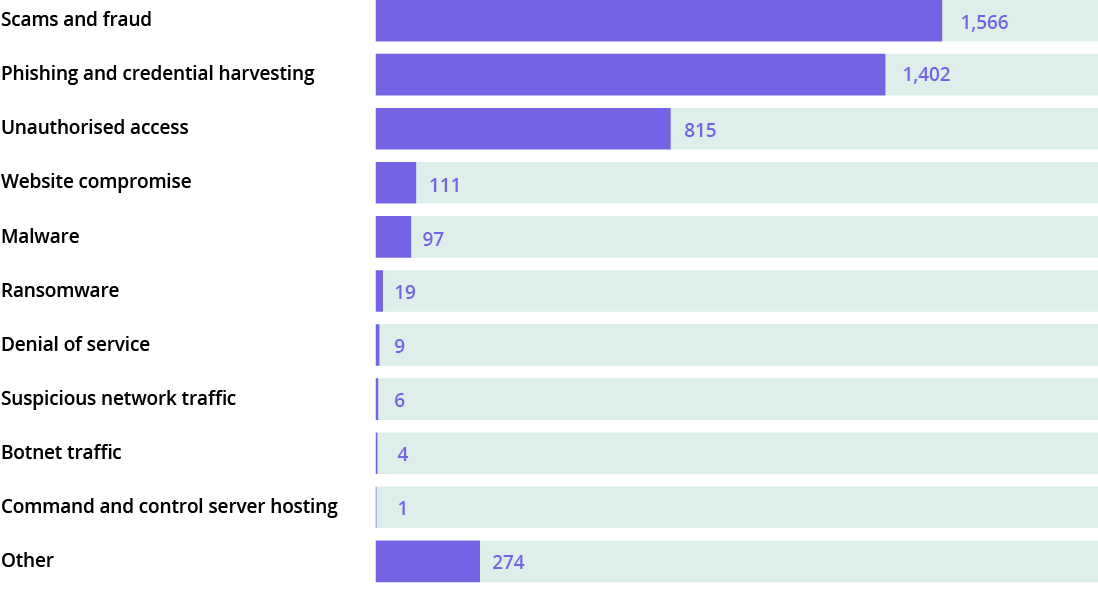
Sub-category breakdown
Financial and other losses
The NCSC records the direct financial loss reported by victims, whether lost to scams or the cost of recovery, where this information is volunteered.
The direct financial loss reported in 2025/2026 totalled $23.8M, decreasing from $26.9 million in 2024/2025.
The NCSC has recorded several types of loss amongst the incidents handled through the general triage process:
- 1278 financial loss incidents: this includes not only money lost as a direct result of an incident, but also the cost of recovery - for example, the cost of contracting IT security services.
- 220 data loss incidents: loss or unauthorised copying of data, business records, and intellectual property.
- 66 reputational loss incidents: damage to the reputation of an individual or organisation as a result of the incident.
- 32 operational impact incidents: the time, staffing and resources spent on recovering from an incident, taking people away from normal business operations.
- 19 technical damage incidents: impacts on services like email, phone systems or websites, resulting in disruption to a business or organisation.
- 67 other loss incidents: includes types of loss not covered in other categories.
Due to the way incidents are handled, not all financial loss information is reported or recorded.
Analysis of incidents of potential national significance
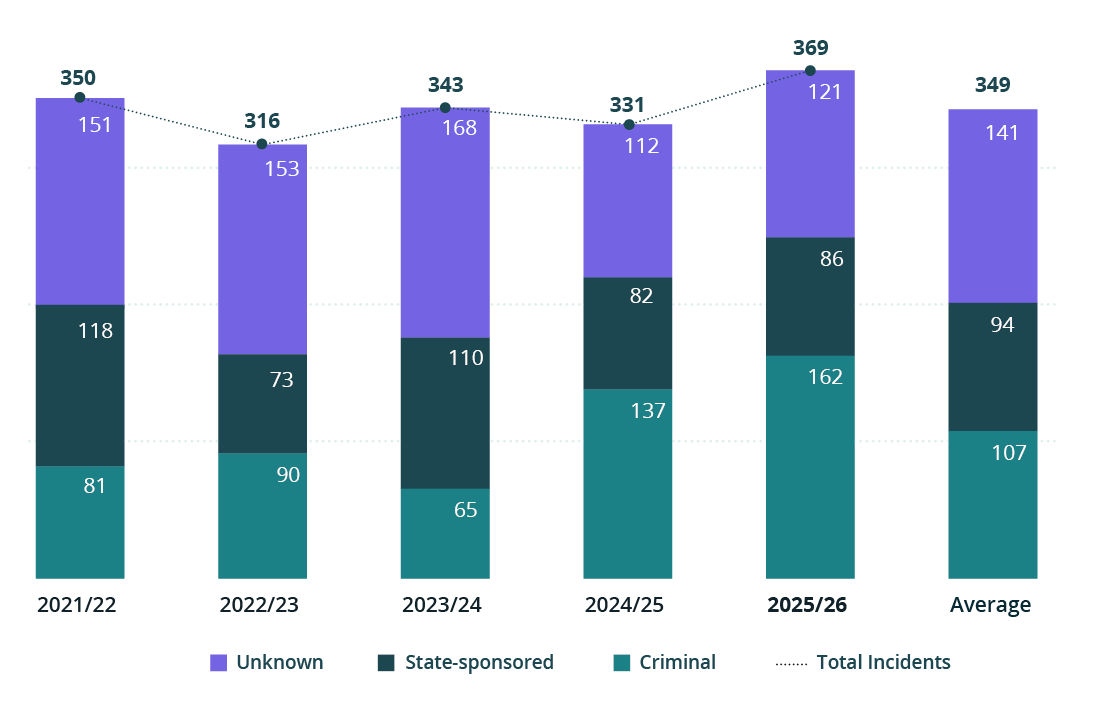
In 2025/26, 369 incidents reported to the NCSC were triaged for specialist support and analysis and are referred to as incidents of potential national significance.
Actor motivations
After several years of decline 2025/26 saw an increase in the total number of incidents of potential national significance handled by the NCSC. An 18% jump in criminal or financially motivated incidents has driven the overall increase.
Out of the 369 reported incidents, 86 indicated links to suspected state-sponsored actors, compared to 82 in the 2024/25 year.
Of the remaining incidents, 162 indicated links to criminal or financially motivated actors, compared with 137 in the 2024/25 year.
The origin of 122 reported incidents could not be attributed.
Breakdown by sector
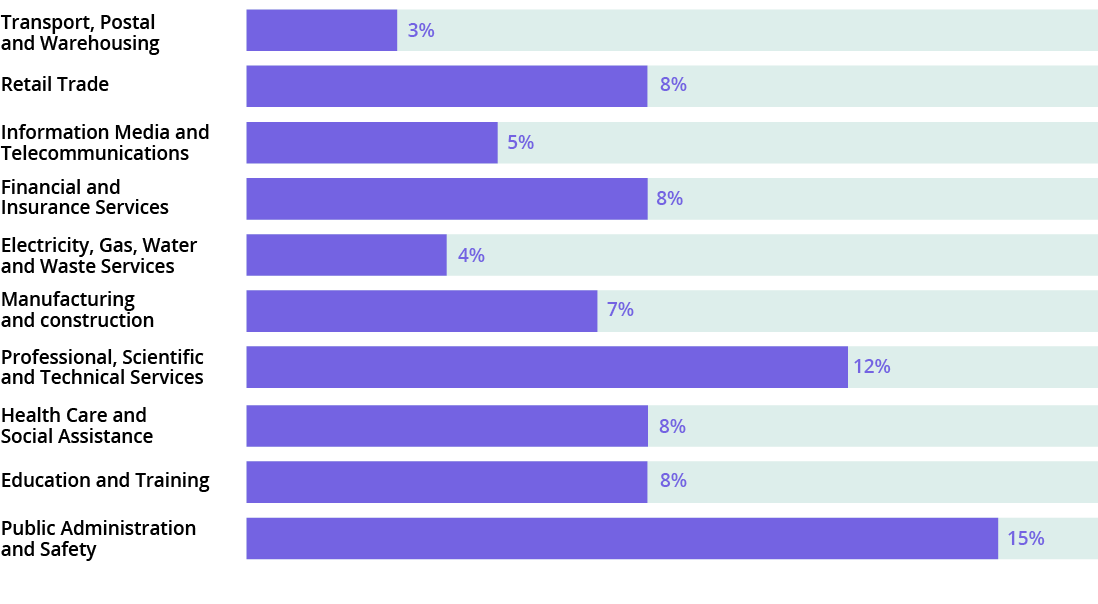
The sectors most affected by incidents of potential national significance during 2025/26 were public administration and safety, health and social assistance and education and training. The public administration and safety sector, made up of central government agencies, local councils, public order and safety services, and defence, experienced a third of these potentially high-impact incidents. The NCSC also observed a doubling of attacks targeting the health care and social assistance sectors and education and training.
Top sectors affected by incidents of potential national significance
Resources
Key cyber security terms and their definitions can be found in our glossary: